How three harmless gaps turn into a total loss
None of the three vulnerabilities would have been a cause for concern on its own.
This is exactly what makes this story so instructive – it shows how individual, inconspicuous details can lead to complete system access. The following process is a typical, composite example that can be found in similar forms time and again in medium-sized IT environments.
Gap one: a forgotten service
An internal file server, set up years ago for a single project, had long been formally replaced. It was hardly used anymore – but it had never been shut down.
The login page ran on the network with a software version that hadn't received updates in a long time. On its own: an old system among many, such as exists in almost every grown IT landscape. No acute alarm, no obvious threat.
Gap Two: A reused password
An IT employee had set a password for this old service years ago – the same password, slightly modified, that he also used for his current administrator account.
This in itself is not uncommon. Password reuse is one of the most underestimated risks, precisely because individual systems are often classified as „not critical enough“ for their own complex password.
Gap three: overly generous authorization
The administrator account itself had, as is common in many mature environments, more extensive rights than would have been necessary for daily use.
A history of acquired responsibilities, never consistently tidied up. That, too, is unexceptional in itself. Such authorization structures can be found in almost every IT department that has grown over the years.
The combination: a complete attack path
Only in combination do these three points, harmless in themselves, become a serious risk.
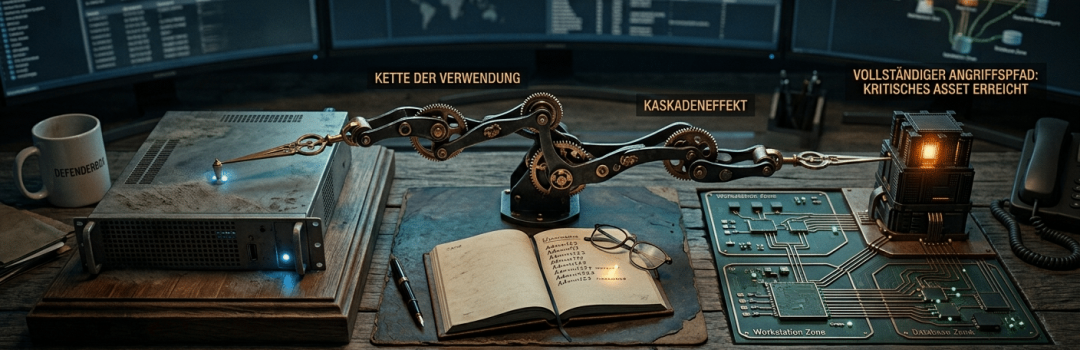
The outdated file server provides the initial access – a known, unpatched vulnerability can be exploited there with publicly available tools. From there, the reused password stored there can be extracted. This password can then be used to access the current administrator account.
And with the generous permissions of this account, the path to central company data is clear.
Three steps, each unremarkable on its own. In sum: a complete, critical attack path that runs from an legacy system to the core of corporate IT.
Why this is so easily overlooked
Classic security reviews that examine individual systems in isolation would likely have rated each of these three vulnerabilities as low to medium – if at all.
Only the consideration of the combination reveals the actual risk.
This is exactly why attack path analyses approach things differently than traditional vulnerability lists: They don't just ask „What is risky on its own?“, but „What can be chained together?“ – and it's precisely this chaining that most often leads to actual damage in practice.
Are you prepared for cyber attacks?
Stay vigilant – your IT is with us!
Image generated by AI