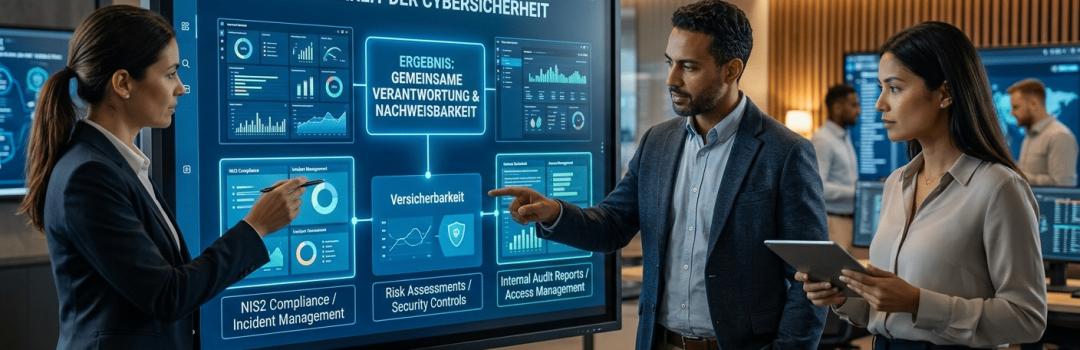
Three perspectives, one common expectation
A sentence that causes discomfort in many IT departments: „Please present your current security credentials.“
Whether they come from a NIS2 auditor, the cyber insurance in the event of a claim, or the internal audit – the reaction is usually the same: a brief hesitation, then the question of what exactly counts as proof.
That is no coincidence. Unlike in a balance sheet review, there is no uniform checklist for IT security certifications that is binding for everyone. Anyone who wants to understand what is actually required must change perspective – away from their own IT operations and towards what is expected on the other side of the table.
What NIS2 inspectors want to see
NIS2 requires affected organizations to implement risk management for their own IT and OT environments, including documentation of regular audits.
What is crucial here is not the perfect result per se, but rather the comprehensibility:
- Has it been tested?
- When was the last time?
- What was done with the results?
A reviewer usually does not want to see a flawless environment – he wants to see that a functioning process exists that detects security vulnerabilities and addresses them. A one-time, undocumented review three years ago does not meet this requirement, even if the results were good at the time.
What cyber insurers want to see
In the event of a claim, an insurance company first checks whether the information provided in the claim regarding IT security corresponds to reality.
It becomes particularly unpleasant here when evidence is lacking:
- Was actually regularly checked for vulnerabilities, as stated in the application
- Or was that a snapshot that was never repeated since then?
Insurers are increasingly interested in the continuity of security measures, not only in the state at the time of contract conclusion.
An up-to-date, repeatable security check is therefore not just a compliance issue; in an emergency, it is also a reason for the insurance company to take action.
What internal auditors want to see
Internally, it often comes down to a third dimension: the ability to be understood by one’s own management.
An internal auditor generally wants to be able to demonstrate that IT risks are systematically identified and prioritized – not on an anecdotal basis, but using a comprehensible methodology.
Here too, it is less important to look at the individual indicators than to consider the underlying structure: a risk assessment that can be compared over several periods of testing shows whether the situation has improved or deteriorated.
The common denominator
However different the three perspectives are in detail, they all lead to the same fundamental question:
Is there any current, repeatable evidence that your own IT security is being systematically reviewed?
Not just a single opinion, but a process with a history.
It is this repeatability that is often the bottleneck. A classic, manually conducted penetration test is complex enough that it rarely takes place more often than once a year – for many of the above requirements, that is not enough.
An automated, regularly performed security check closes this very gap: it provides the continuity that inspectors, insurers, and auditors alike expect.
Are you prepared for cyber attacks?
Stay vigilant – your IT is with us!
Image generated by AI