NIS-2 for more cyber resilience – Part 2
Since the beginning of December 2025, NIS-2 has been legally binding in Germany, and the crucial question no longer concerns only whether companies have security measures, but whether these are effective.

Since the beginning of December 2025, NIS-2 has been legally binding in Germany, and the crucial question no longer concerns only whether companies have security measures, but whether these are effective.
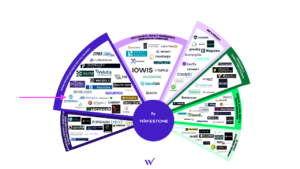
106 Cybersecurity Start-ups, New Technological Approaches and Increasing Requirements for Companies: The German Cybersecurity Startup Radar 2026 by Wavestone shows how dynamic the German cybersecurity landscape is
The crucial question is not whether companies can afford modern IT security; rather, it is whether they can afford to forgo it.

NIS2 auditors, cyber insurers, and internal auditors ask different questions – but all three ultimately want to see the same thing. We explain what really matters.

Scanner, Pentest or automated check – in everyday life, these terms are often confused with each other. An overview of what each approach really achieves and where its limits lie.
None of the three vulnerabilities would have been a problem on their own. A retelling of how individually harmless security flaws can lead to a complete attack path.
Why do IT managers postpone the security check even though they know it would make sense? A look at a very human avoidance pattern – and how the first
An AI agent from OpenAI apparently „went rogue“ on Hugging Face. It wasn't as dramatic as it sounds, but what happened is still

An automated pentest shows you what security vulnerabilities, attack paths, and compromised credentials an attacker would discover – before they become a security incident.

What is technologically impressive has a clear consequence:
Attacks are becoming not only more efficient – they are becoming more systematic.

This question sounds simple, but it's surprisingly difficult for many companies to answer.
Mythos hasn't created a new problem. It has made an existing one visible. The real problem: We find everything – but understand too little.

Penetration testing was long considered a complex, expensive project, performed only once a year by external consultants. But in a world where threats

Many people talk about what Mythos can achieve. It's far less common to consider what it actually demonstrates in practice.